Rank Math PRO Supply-Chain Attack Backdoored WordPress Sites via Compromised Plugin Downloads
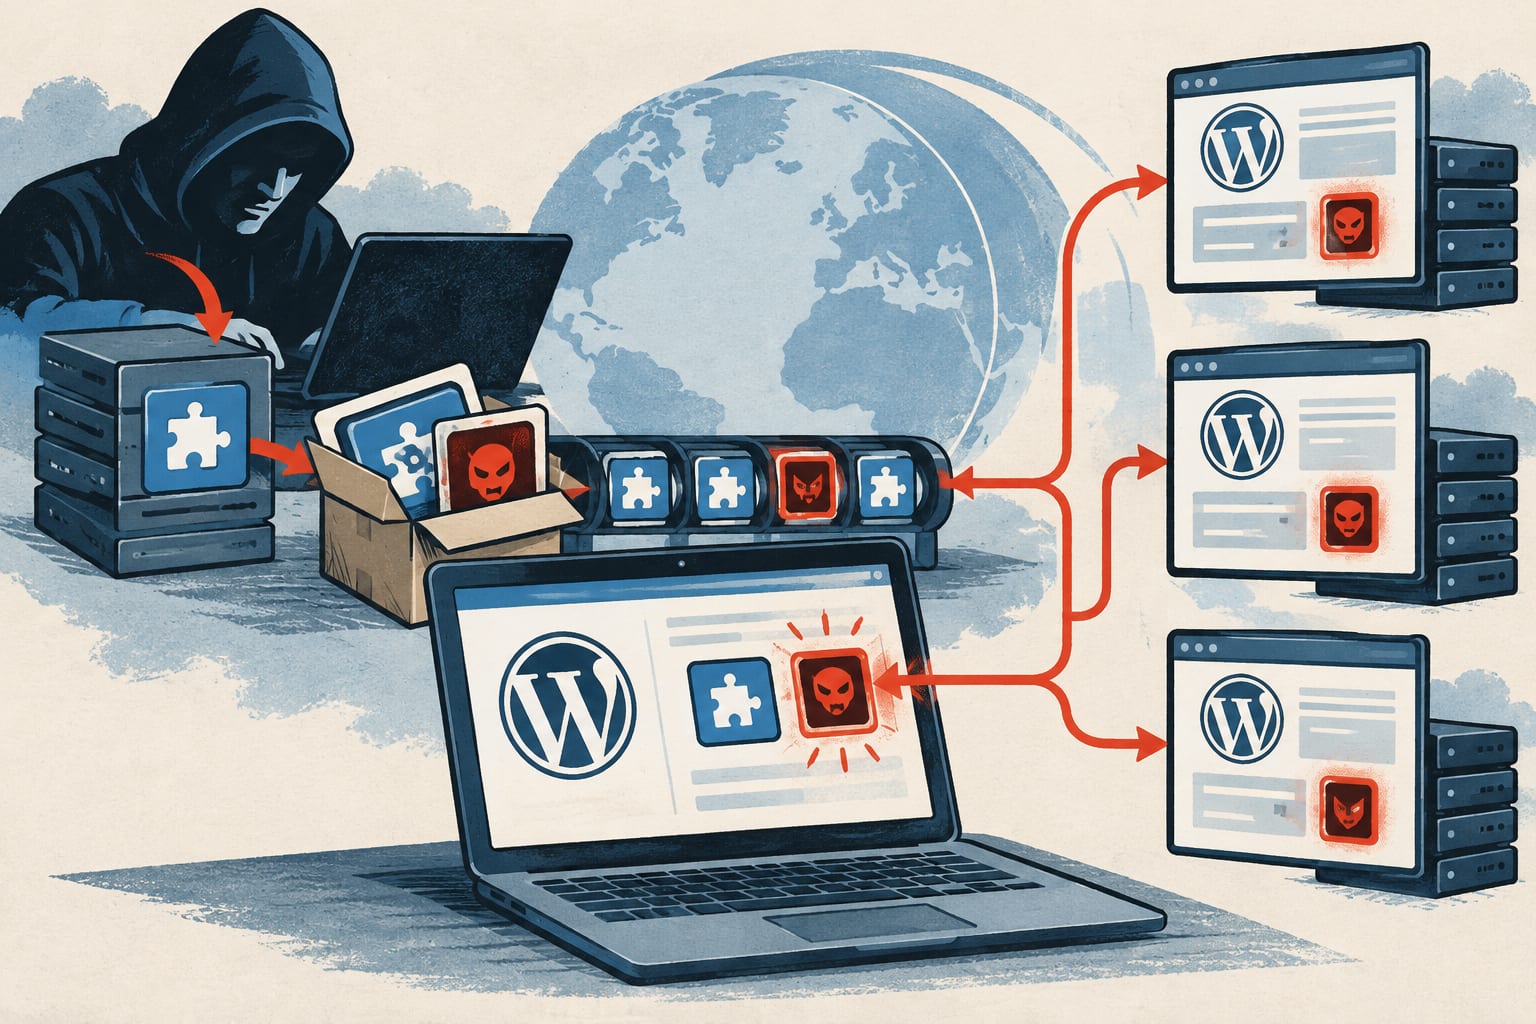
A supply-chain attack against the Rank Math PRO WordPress plugin planted hidden backdoors on websites that downloaded a trojanized build directly from the vendor's own site, according to a report from BleepingComputer. The incident affects site owners and administrators who use the paid version of the popular SEO plugin, which underpins the free Rank Math SEO tool active on more than 4 million WordPress installs.
Rank Math disclosed that a limited set of users who downloaded version 3.0.123 of Rank Math PRO between October 15 at 20:02 UTC and October 16 at 07:12 UTC received compromised files. The vendor said the affected plugin files contained malware capable of compromising a website once the plugin was activated. Rank Math stated it removed the malicious files and shipped a clean release, version 3.0.124, after discovering the issue. Only the PRO version was affected; the free Rank Math SEO plugin distributed through WordPress.org was not touched.
According to Rank Math's advisory, the malware establishes persistent access on infected sites, communicates with a domain identified as rank1cdn[.]com, and is capable of recreating hidden backdoors whenever someone visits the compromised website. The vendor warned that database credentials, API keys and other secrets accessible to the web server could be exposed as a result.
As a senior editor at a trade publication covering this space for people who manage WordPress infrastructure day to day, it is worth noting that BleepingComputer's own research turned up a related artifact during its investigation. The outlet found a PHP malware sample on VirusTotal named "cache-preloader-fff033 (1).php" that shares indicators of compromise with the Rank Math alert, including the same XOR obfuscation key, the same WordPress database entry marker, the same cron job marker, and code that creates administrator accounts using a specific username prefix and email domain pattern. That file was not referenced in either the Rank Math or Wordfence advisories. BleepingComputer said the sample appears to function as a first-stage script that deploys the backdoor file named in Rank Math's own advisory, and that it includes capabilities to execute commands, modify WordPress databases, and steal cloud credentials from AWS, Cloudflare, Google Cloud and Azure, along with SSH keys and other sensitive data. The outlet could not confirm whether this specific file was distributed through the compromised plugin itself, though the shared indicators point to the same threat actor.
Impact
Rank Math did not respond to BleepingComputer's request for details on how many sites were affected or how the attacker initially gained access to the vendor's distribution files. The compromise window was narrow, roughly 11 hours, but any site that downloaded and activated the plugin during that period should be treated as compromised. Rank Math's guidance makes clear that simply deactivating or updating the plugin will not remove the threat once it has taken hold, meaning affected operators face a more involved cleanup than a routine patch cycle. For sites with clean backups, the remediation path is restoring files and databases, running security scans, and rotating all passwords, keys and salts. For sites without a safe backup, Rank Math is recommending manual removal of the entire plugin folder and any malicious database entries, followed by an audit for additional backdoors, unauthorized administrator accounts, altered files, scheduled tasks and changes outside the WordPress installation itself.
What to watch
Site administrators should check whether Rank Math PRO was downloaded and activated between October 15 at 20:02 UTC and October 16 at 07:12 UTC and treat any match as a confirmed compromise. Outbound connections to rank1cdn[.]com should be blocked. Anyone who installed but never activated the plugin should delete it and reinstall the clean 3.0.124 build before scanning. Given the unconfirmed but indicator-linked PHP sample BleepingComputer uncovered, administrators should also watch for unfamiliar administrator accounts using the "wpsupport_" prefix or "@wp-mail.net" addresses, and for the "wp-includes/class-wp-cache-util.php" file referenced in Rank Math's advisory. Further detail from Rank Math on the scope of affected sites and the root cause of the breach remains outstanding.
Site owners should be wary of downloading any auto backlink tool wordpress plugin from unofficial sources, since compromised downloads can quietly install backdoors like the one found in Rank Math PRO.
Many site owners who install unofficial copies just to get backlinks rank math features for free end up exposing their WordPress sites to hidden backdoors.
Source: BleepingComputer
Read our previous article: Social Funnel Marketing Expands AI SEO Services for Home Service Contractors