Fake PuTTY Site Uses Ethereum Smart Contract to Hide Malware Infrastructure
A malicious campaign disclosed on October 12 is using SEO poisoning to push a trojanized PuTTY installer to victims searching Google for the SSH client, then relying on an Ethereum smart contract to manage its command-and-control infrastructure. The technique, known as EtherHiding, lets attackers change server addresses without touching the malware already running on compromised machines, complicating takedown efforts for defenders who rely on static domain blocklists.
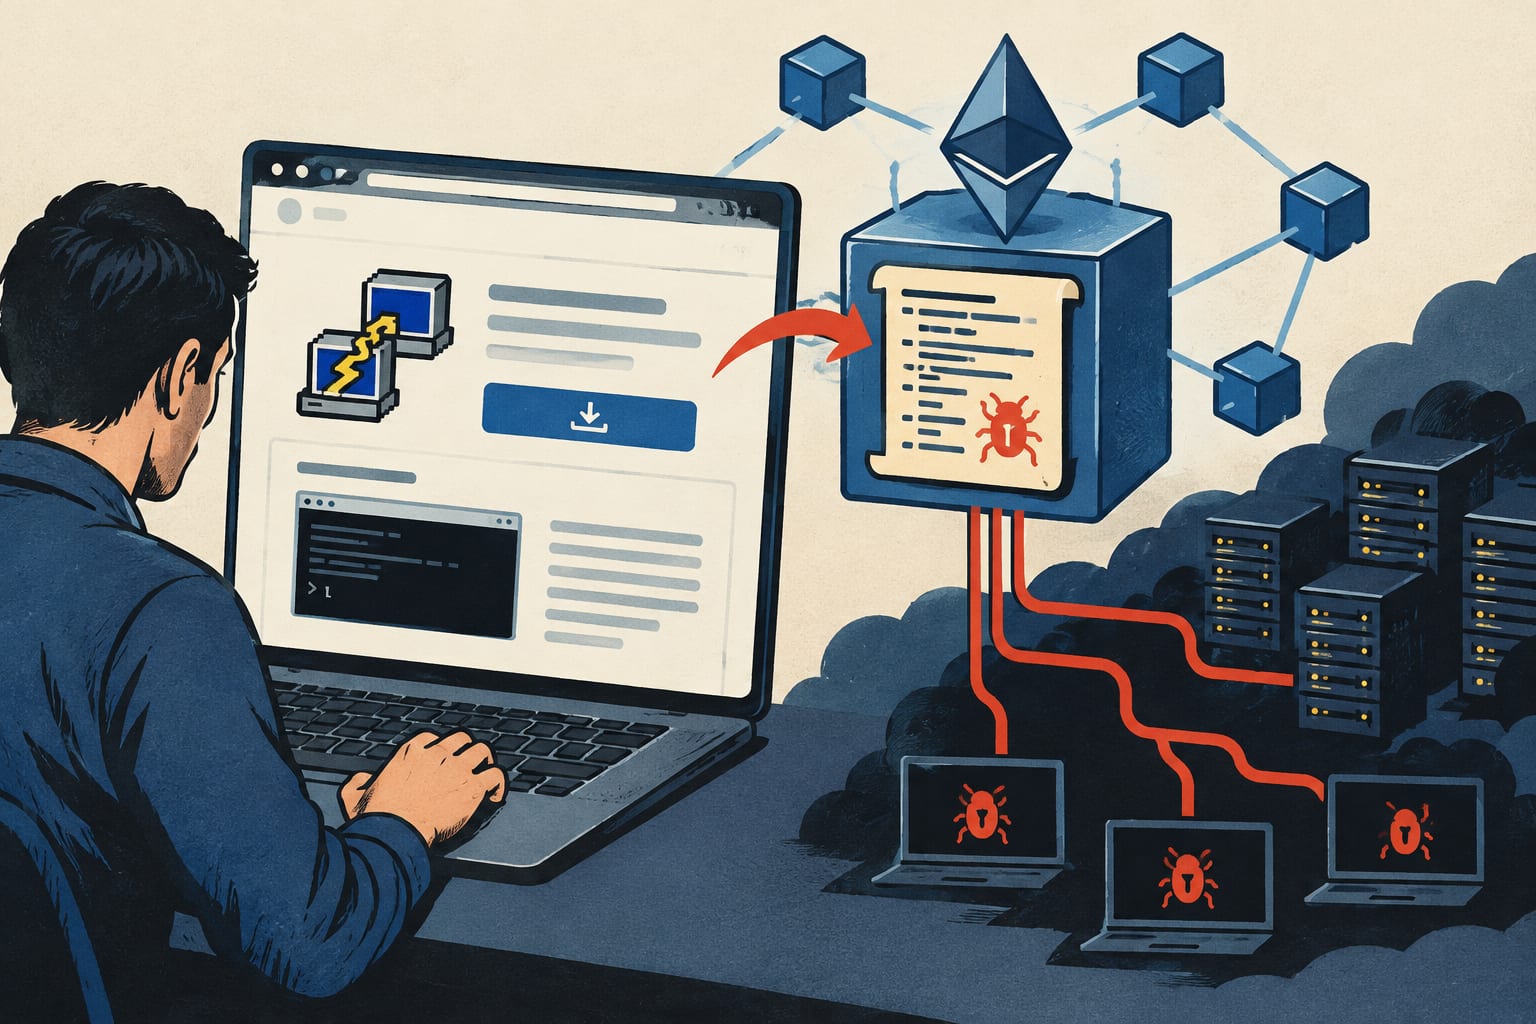
The campaign targets users searching for "PuTTY" or "PuTTY download." A high-ranking search result routes victims to a spoofed page observed at puty.ink, which mimics the title of PuTTY's legitimate download page. The site serves a file called Putty-x86_64.msi from third-party cloud storage rather than PuTTY's official release channel.
Running the installer drops four files into the user's local application-data directory. One is a genuine, Sectigo-signed copy of PuTTY 0.85, which opens and functions normally, giving the victim no visible reason to suspect a problem. The other three files form a malicious loader chain operating silently in the background.
That chain starts with a batch script that hides its console window and checks for an existing Node.js installation. If none is found, it pulls the legitimate Node.js 18.20.5 runtime directly from nodejs.org. A JScript trampoline then uses that runtime to launch an obfuscated JavaScript payload, a "bring your own interpreter" method that leans on legitimate software to execute malicious code and avoids relying on a flagged executable.
Instead of calling a fixed server, the malware queries an Ethereum mainnet smart contract using JSON-RPC eth_call requests, checking seven public RPC endpoints and selecting whichever URL appears most often. It validates the result as a proper HTTP, HTTPS or WebSocket address, refreshes it every five minutes, and keeps a hardcoded fallback in reserve. Researchers at Unit 42 said the installer uses the genuine PuTTY app as a decoy while quietly standing up this Node.js-based loader. Earlier reporting has already documented EtherHiding as a method for retrieving malicious infrastructure or code through smart contracts.
Once connected, the loader polls its C2 server every 500 milliseconds, disguising the traffic as requests for static assets like images or stylesheets. Palo Alto researchers found that any response larger than 10 bytes is executed as JavaScript with full access to Node.js functionality, giving operators a flexible channel to push new capabilities without reinstalling the original payload. Observed commands collected Windows version, locale, graphics hardware, installed antivirus products, domain membership and SMB session data. The malware also exfiltrated browser profiles and session cookies, with reported transfers reaching hundreds of megabytes, and operators installed a WebSocket package alongside a PowerShell loop capturing roughly five screenshots per second for near-live monitoring.
Impact
EtherHiding does not make the malware or its network traffic undetectable. Endpoints, requests and contract interactions can still give investigators a trail. But the approach raises the cost of disruption for defenders who focus only on blocking a conventional, hardcoded C2 domain, since operators can rotate infrastructure through the smart contract without redistributing malware. The reporting does not identify who is behind the campaign or how many systems have been compromised. Risk is heightened for technical users, since PuTTY is often used to reach internal servers shortly after installation, exposing credentials and session data tied to those systems.
What to watch
Security teams should treat unexpected Node.js runtimes appearing in user-profile directories as a red flag, along with unusual msiexec.exe-to-cmd.exe chains and hidden wscript.exe launches. PuTTY's official release page currently lists version 0.85 and its signed 64-bit installer, which should be the only trusted source for downloads rather than search ads or unfamiliar mirrors. If a suspect installer has already run on a host, isolate the machine, review browser-session exposure, and rotate any credentials or tokens that may have been accessible from that system. As a senior editor covering this space daily, this campaign is a reminder to revisit how your organization verifies installer signatures before deployment, since blockchain-based C2 is likely to keep showing up in future loader campaigns.
Attackers behind lookalike download sites often try to get backlinks from forums and search results to push their fake pages higher in rankings.
Attackers often boost fake download pages in search results with an auto backlink tool, which helps a malicious PuTTY clone outrank the legitimate site.
Attackers often rely on a shady seo backlinks builder to push fake PuTTY download pages up search results, tricking unsuspecting administrators into installing malware.
Source: GBHackers News
Before this, we covered: The hidden cost of lost backlinks: How businesses can protect their digital PR investment