


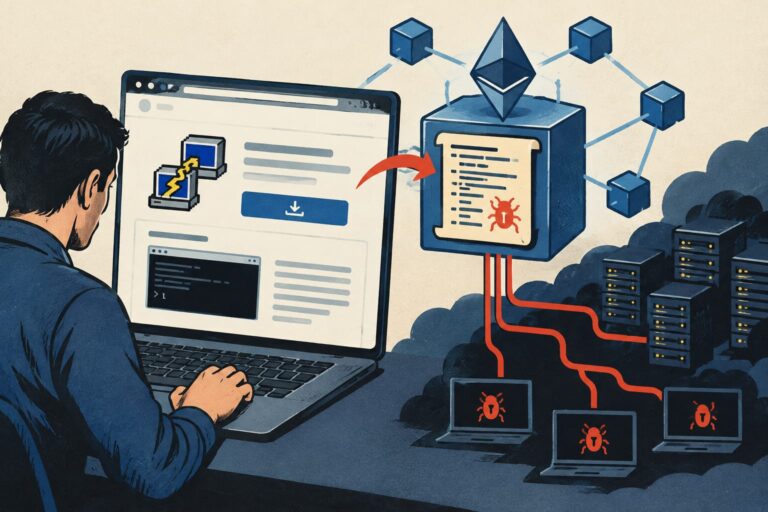
Fake PuTTY Site Uses Ethereum Smart Contract to Hide Malware Infrastructure
A malicious campaign disclosed on October 12 is using SEO poisoning to push a trojanized PuTTY installer to victims searching Google for the SSH client, then relying on an Ethereum smart contract to manage its command-and-control infrastructure. The technique, known as EtherHiding, lets attackers change server addresses without touching the malware already running on compromised…